Newsroom
FlashLoopAdapter Access Flaw Drains $305,000 From Two Aave-Linked Safe Wallets
2 October, 2026 / News / AI / Tags: aave, flashloopadapter, attacker, module, adapter
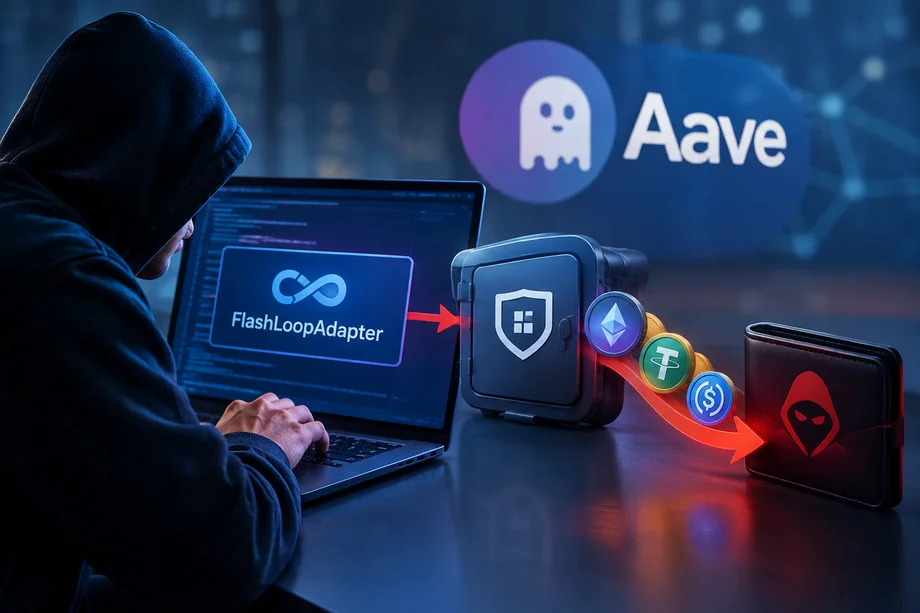
A third-party Safe module for leveraged Aave v3 positions was exploited on Ethereum on October 1, allowing an attacker to extract roughly 114 ETH after bypassing authentication checks
An attacker exploited a vulnerability in the FlashLoopAdapter contract, a custom Safe module designed to open and close leveraged positions on Aave v3, draining an estimated $305,000 from two Safe wallets on Ethereum. The incident, detected at 15:08:57 UTC on October 1, 2026, involved an access-control bypass rather than any flaw in Aave’s core lending contracts.
Security researchers from SlowMist and Defimon Alerts identified the root cause in the adapter’s open() and close() functions. These functions checked whether ISafe(msg.sender).isModuleEnabled(address(this)) returned true. An attacker deployed a fake Safe contract programmed to always return true, thereby gaining unauthorized access to the module’s execution path.
How the Attack Unfolded
Once the forged authentication succeeded, the attacker controlled the adapter’s _swap() function and supplied a custom swap router and calldata. The router was set to one of the victim Safe addresses, and the calldata invoked execTransactionFromModule. Because FlashLoopAdapter was already enabled on the target wallets, the call was accepted as a legitimate module transaction.
The attacker first took a Morpho WETH flash loan and used the borrowed funds to repay approximately 1,335 WETH of outstanding Aave debt on the larger Safe wallet, address 0xcfedf95a3653a128dfc2e4288758a1a1850d169f. Debt repayment unlocked the associated collateral, allowing the withdrawal of roughly 1,306 weETH to an attacker-controlled address. A second Safe, 0xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520, lost an additional 6.4 weETH through the same path.
Both affected Safes shared a single owner. After settling the flash loan and converting part of the withdrawn weETH, the attacker retained approximately 114.09 ETH, valued at about $305,000 at the time of the reports. SlowMist listed the attacker address as 0x42c2633438609881c8fBAb82414eb9A0c45F9353 and the vulnerable FlashLoopAdapter contract as 0x16bb8b912da187870c23ec6756bb3fad061283d8.
Aave Core Protocol Unaffected
Aave founder and CEO Stani Kulechov stated that the compromised contract was a third-party external adapter built on top of Aave and had no impact on Aave v3 itself. Defimon Alerts and SlowMist both confirmed that the core Aave v3 lending pools and contracts remained intact throughout the incident.
FlashLoopAdapter functioned solely as a convenience layer for automating leveraged looping strategies within Safe wallets that had enabled the module. Safe modules can execute transactions without requiring repeated owner approvals, a design that supports automation but also creates a pathway to wallet assets once authentication is bypassed.
Net Loss Versus Gross Transaction Volume
Reports noted that the gross value of assets moved in the transaction appeared significantly higher, with one Etherscan record citing roughly $3.88 million. That figure represented the full collateral flow required to repay debt and unwind the leveraged position. The attacker’s actual net proceeds after loan repayment and swaps totaled approximately 114 ETH.
The investigation into whether additional wallets that enabled the same module were affected remains ongoing. No recovery efforts or further technical updates had been publicly detailed at the time of the initial reports.
Disclaimer
This article was generated by AI using information from multiple industry sources. It has not been reviewed or verified by a human editor and may contain inaccuracies, omissions, or misinformation. Readers are encouraged to independently verify any information before making decisions based on its content.Tired of the noise?
Let the bots trade for you.
Trade 24/7, without emotion, with data-driven strategies.
Associated articles
Aave Plans to Deprecate 75 Low-Adoption Reserves and Exit Six Blockchains
Aave Founder Stani Kulechov Denies Kraken Stake Sale at Steep Discount
Aave V4 Enables USDC Loans Against Coinbase Tokenized Stocks on Base

Aave V4 Launches on Avalanche to Support Tokenized Asset Lending

Kraken in Talks for 15% Stake in Aave at $385 Million Valuation
Latest articles
QNT Token Goes Live on Solana via Sunrise and Raydium
Bitcoin Treasury Firms Face Uphill Battle Against Strategy, Says Ammous
Crypto Hacks Drain $1.26 Billion in Q3 as September Losses Hit Yearly High
Bitcoin Policy Group Challenges MSCI Index Rules Targeting Crypto Treasury Firms