Newsroom
Binance Confirms EIP-7702 Use in Record $6.3 Billion Hot Wallet Theft
30 October, 2026 / News / AI / Tags: eip, binance, teng, attackers, delegation
Exchange CEO details how attackers leveraged the Ethereum feature after initial access via a compromised device, as the firm moves to cover losses and restore services
Binance, one of the largest cryptocurrency exchanges, has confirmed that attackers employed Ethereum’s EIP-7702 feature during a sophisticated breach that drained roughly $6.3 billion from its hot wallets. The incident, which unfolded primarily on October 29, 2026, ranks as the largest crypto theft on record and affected assets across 10 blockchains, with the bulk of the transfers completed in about 20 minutes.
Chief Executive Richard Teng described the operation as a complex attack that went beyond the compromise of a single engineer’s laptop. Investigators later identified additional points of breach. Teng stated that hackers used a self-destruct mechanism to erase evidence and applied EIP-7702 account delegation on Ethereum to gain control of a hot wallet, allowing them to bypass ordinary approval processes.
How EIP-7702 Works and Why It Matters
EIP-7702, formally titled “Set Code for EOAs,” became active as part of Ethereum’s Pectra upgrade on May 7, 2025. Proposed by Ethereum co-founder Vitalik Buterin and other developers, the change lets ordinary externally owned accounts temporarily adopt the code of a smart contract while retaining their original address and balances.
Users authorize the temporary link through a new transaction type that carries signed authorizations naming a target contract. Once processed, a delegation indicator points the account to that code. From that point, any call to the account executes the contract’s logic with unrestricted access to the account’s funds. The delegation remains in place until the owner signs a new authorization that either redirects or clears it.
The design aims to deliver three practical capabilities without forcing users to migrate to new account types: transaction batching, fee sponsorship by third parties, and the creation of limited-permission keys. At the same time, the specification itself cautions that delegated code receives full control of the account and that no safe user-facing interface exists for authorizing such delegations.
Security researchers noted problems soon after activation. Within weeks, analysis showed that a large majority of early EIP-7702 delegations pointed to nearly identical malicious contracts designed to drain compromised wallets automatically.
The Ethereum Component of the Binance Breach
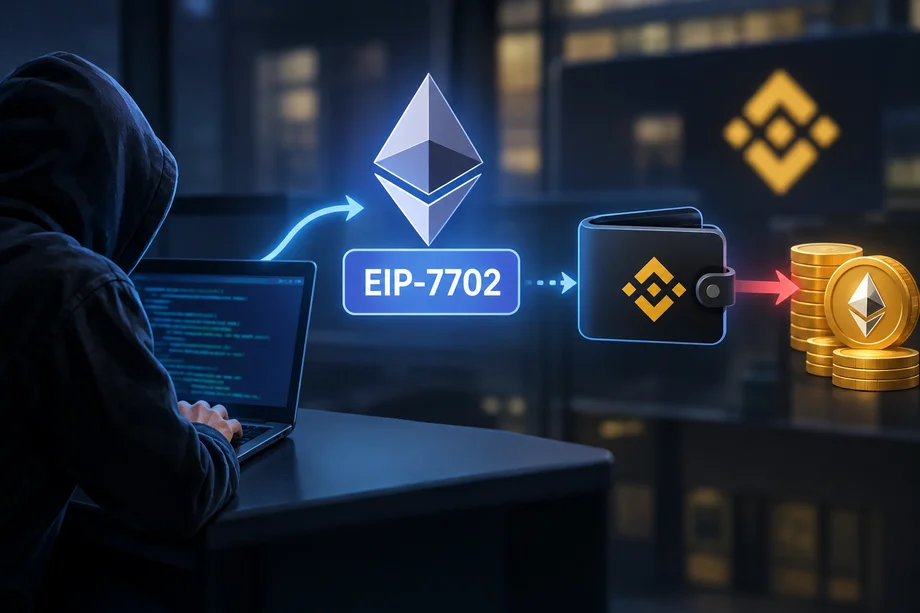
Blockchain analytics firms reported that the attackers submitted approximately 50 pre-signed EIP-7702 authorizations for a Binance hot wallet. An operational wallet, previously funded through the Tornado Cash mixer, broadcast those authorizations. The result converted the exchange wallet into a controlled “sweeper” that transferred assets to addresses under the attackers’ control.
Teng and external investigators stressed that valid signatures from the compromised account were still required. Parallel withdrawals from Binance wallets on the other nine chains occurred through ordinary signed transfers. This pattern indicates a deeper compromise of the exchange’s hot-wallet signing infrastructure rather than a protocol-level defect in Ethereum itself.
Binance has stated that private keys for the wallets did not appear to have been leaked. Security specialists noted that once the attackers could propose transactions to a secure signer, EIP-7702 simply allowed the entire drain to occur in a single sweep and may have helped circumvent certain internal checks that would otherwise have required multiple separate transactions.
Attribution and Broader Context
Two major analytics firms independently attributed the theft to the North Korean group known as TraderTraitor, the same cluster previously linked to the $1.5 billion Bybit incident earlier in 2025. The firms cited both on-chain patterns and additional intelligence in reaching that conclusion with high confidence.
The scale of the loss—estimated between $6.3 billion and $6.4 billion depending on the precise valuation window—makes it the largest single crypto theft recorded to date.
Binance Response and Recovery Steps
Binance immediately suspended withdrawals while it rebuilds and tests infrastructure. The firm is reviewing cloud environments, employee devices, private-key handling, and transaction-signing procedures. Teng indicated that withdrawals are expected to resume by the following Sunday, roughly 40 hours after the latest public updates.
The exchange has pledged to make customers whole using corporate reserves. It reported holding more than $6.34 billion in total reserves earmarked for the purpose, of which approximately $5 billion was already denominated in the affected cryptocurrencies. The remaining amount is being acquired through exchanges and over-the-counter markets.
An initial proof-of-reserves disclosure is planned before a fuller report scheduled for Monday. Binance is also coordinating with law-enforcement agencies, blockchain investigators, and token issuers in efforts to recover assets.
Security Experts Assess the Role of EIP-7702
Ido Ben-Natan, co-founder and chief executive of blockchain security firm Blockaid, said the root cause was almost certainly a compromised signing system rather than the Ethereum feature itself. Attackers could have extracted the funds without EIP-7702, he noted, though the upgrade allowed a single-sweep approach that may have bypassed certain safeguards.
Ivo Georgiev, co-founder of Ethereum wallet provider Ambire, observed that once the attackers possessed the ability to authorize transactions, EIP-7702 made only a marginal difference to the outcome. He added that the feature remains poorly understood by many operators and that engineers recovering control of systems may overlook the need to revoke a malicious delegation.
Both specialists warned that similar signing-infrastructure attacks remain a realistic threat to other exchanges. Transaction simulation before approval was cited as one practical defensive measure that could flag malicious requests earlier in the process.
Binance continues its internal investigation while working with external partners. The exchange has reiterated that the compromised wallets were its own hot wallets rather than segregated customer funds, though some of those wallets had previously been listed among assets supporting customer balances.

Disclaimer
This article was generated by AI using information from multiple industry sources. It has not been reviewed or verified by a human editor and may contain inaccuracies, omissions, or misinformation. Readers are encouraged to independently verify any information before making decisions based on its content.Tired of the noise?
Let the bots trade for you.
Trade 24/7, without emotion, with data-driven strategies.
Associated articles
North Korean Lazarus Group Suspected in $6.3 Billion Binance Hack
CoinDCX Confirms Losses After Suspicious $16M Transfers From 2025 Hack Wallets
Binance to Resume Withdrawals by Nov. 1 After Hot Wallet Security Review
Binance Faces $6.3 Billion Security Breach, Freezes $3 Billion in Crypto Assets
Elon Musk Warns Superintelligent AI Agents May Seize Crypto Independently After Binance Breach
Latest articles
Chevron Profit Nearly Triples to $9.9 Billion as Refining Hits Record Levels
Elon Musk Warns Superintelligent AI Agents May Seize Crypto Independently After Binance Breach
Aave Freezes 292 Lending Reserves After Binance-Linked Wallet Borrows Against Stolen USDT
Binance Partners With FBI and Secret Service After $6.3 Billion Security Breach