Newsroom
Coldcard Exploiter Shifts 45% of Wave 3 Bitcoin Through Mixing and Cross-Chain Transfers
7 September, 2026 / News / AI / Tags: vaults, coinjoin, wave, btc, vault
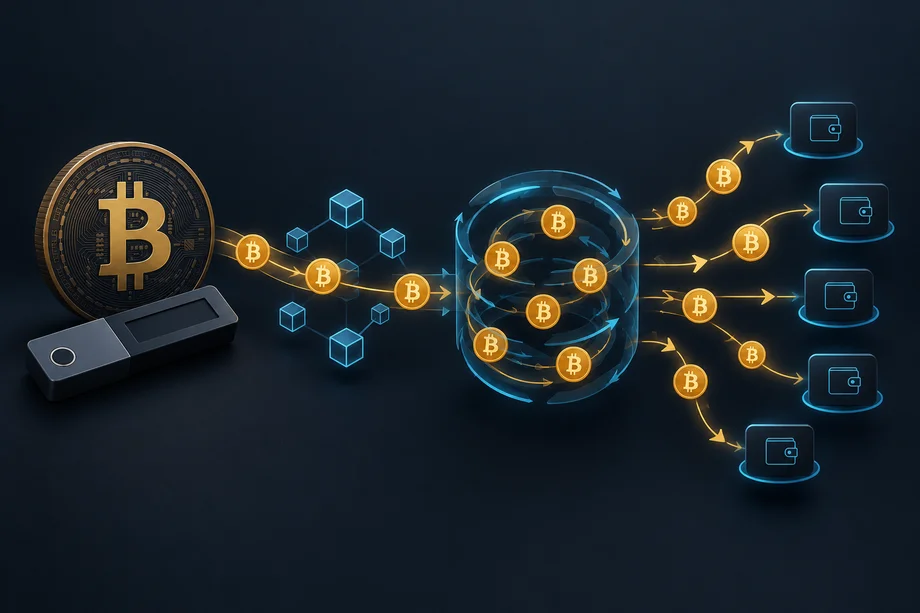
The attacker behind a series of hardware wallet thefts has moved 97.09 BTC valued at roughly $7.7 million from the largest Wave 3 vaults using THORChain and CoinJoin transactions
More than a month after the Coldcard hardware wallet exploit first came to light, the operator linked to the third wave of thefts continues to relocate stolen Bitcoin. On-chain analysis shows the individual has systematically transferred funds from the largest of 293 attacker-controlled multisignature vaults, employing both cross-chain swaps and privacy-enhancing mixing techniques.
Structured Vault System and Systematic Withdrawals
In Wave 3 the attacker consolidated approximately 208.24 BTC from roughly 1,912 victim addresses into 293 separate 2-of-2 multisig vaults. Each vault was funded by a collection address corresponding to one or more compromised wallets. The vaults were then ranked by original balance, and withdrawals have followed that ranking from largest to smallest.
The first significant movement occurred on September 2, when 20.50 BTC from the largest vault was routed through THORChain and converted into Ethereum. The receiving Ethereum addresses were later emptied. On September 5 the second-largest vault sent 15.48 BTC into a CoinJoin transaction. The following day an additional 61.12 BTC from ten more vaults entered CoinJoin rounds, some via intermediate addresses.
Across these three transfers the attacker moved 97.09 BTC within five days. That sum represents about 45 percent of the 214.07 BTC originally held in the Wave 3 vaults, leaving approximately 116.98 BTC still unmoved.
Possible Expansion of Wave 3
Researchers also identified a previously unknown vault that followed the same 2-of-2 multisig pattern and later linked to a CoinJoin. The vault drew funds from 58 addresses. If confirmed as part of the same campaign, the Wave 3 total would rise to 294 vaults and the overall amount tied to the Coldcard exploit would increase to around 1,806 BTC, valued at approximately $143.9 million.
The next ten untouched vaults currently hold a combined 30.81 BTC, while the smaller vaults ranked 61 through 293 contain 33.77 BTC in total. This concentration of remaining balances in lower-ranked addresses indicates the attacker is still prioritizing the larger holdings.
Origin of the Vulnerability
The thefts stem from a firmware flaw introduced in a 2021 update to certain Coldcard devices. The bug reduced the randomness of the seed-generation process, allowing private phrases to be brute-forced and single-signature wallets to be drained remotely without physical access to the hardware. Incidents began on July 30 and were later grouped into distinct waves based on transaction patterns and address clustering.
By mid-August researchers had linked roughly 1,779 BTC to 190 victims across more than 8,600 addresses. The possibility of a fourth wave has been noted but remains unconfirmed. Most of the stolen Bitcoin continues to sit in identifiable attacker-controlled addresses, allowing ongoing monitoring even as CoinJoin transactions complicate direct attribution of individual outputs.
The pattern of withdrawals—largest vaults first, followed by successive CoinJoin rounds—points to an organized process rather than random liquidation. Further movements from the remaining vaults are expected as the operator works through the ranked list.


Disclaimer
This article was generated by AI using information from multiple industry sources. It has not been reviewed or verified by a human editor and may contain inaccuracies, omissions, or misinformation. Readers are encouraged to independently verify any information before making decisions based on its content.Tired of the noise?
Let the bots trade for you.
Trade 24/7, without emotion, with data-driven strategies.
Associated articles
Coldcard Attacker Begins Converting Stolen Bitcoin to Ether via THORChain

Galaxy Research Puts Coldcard Wallet Losses Near $130 Million as Fourth Attack Wave Emerges

Bitcoin Holders Shift $15 Billion After Coldcard Firmware Exploit

Coinkite Issues Urgent Coldcard Warning After $38 Million Bitcoin Drain

Small Bitcoin Transfers Reach Highest Level Since FTX Amid Coldcard Wallet Incident
Latest articles
El Salvador Denies Government Backing for New Sivar Remittance App as Stablecoin Shift Accelerates
Goldman Sachs Puts $100B Treasury Fund on Avalanche Rails
Cboe Extends S&P 500 Options Deal to 2051 as Tokenized Contracts Move Closer
Greece Joins EU Crypto Rules With Four Providers