Newsroom
Hidden Chip in CryptoBilis Sold Ledger Signers Captures Recovery Phrases and Sends Them Over LTE
13 October, 2026 / News / AI / Tags: cryptobilis, ledger, devices, reseller, implants
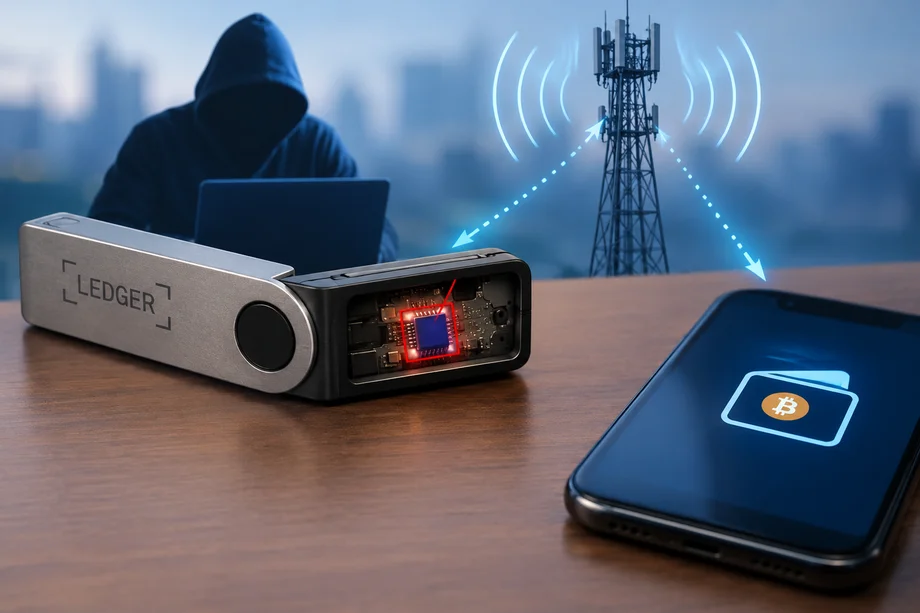
Ledger confirms unauthorized implants in some devices sold by Southeast Asian reseller allow attackers to steal 24-word recovery phrases during setup and transmit them via cellular network, prompting immediate security warnings and distributor suspension
Ledger Details Technical Operation of Unauthorized Implants
Ledger's Donjon security research team has identified unauthorized hardware components installed inside certain cryptocurrency signers distributed by CryptoBilis. These implants sit within the device casing and monitor the display during the wallet initialization process. When the screen shows the 24-word recovery phrase, the component decodes the information using an internal microcontroller before sending the data over an LTE connection with an embedded SIM.
The implant functions separately from the signer's core security systems. It does not modify the Secure Element, the operating system, cryptocurrency transactions, or digital signatures. Ledger researchers determined that the component reads display output during setup without altering the underlying signing process. All verified fund losses so far trace back exclusively to devices purchased through CryptoBilis.
Ledger has not confirmed the total number of affected users or the overall value lost. Third-party blockchain analytics estimates range from $86 million to more than $100 million, but the company states these figures require independent verification and do not yet represent confirmed totals.
Distribution Incident Triggers Immediate Response
CryptoBilis received reports of cryptocurrency losses on October 9. Ledger immediately requested that the reseller halt sales and shipments of its products. The distributor confirmed the suspension of Ledger signers and later extended the stop to all hardware wallet brands sold in Indonesia, Malaysia, and the Philippines. CryptoBilis also closed its physical stores temporarily and is working with independent specialists to review its processes.
Other hardware wallet manufacturers reacted quickly. Trezor removed CryptoBilis from its authorized reseller network after confirming no tampering reports tied to its devices. OneKey terminated the reseller agreement, suspended new reseller onboarding, and began reviewing its existing distribution network while offering free replacements for affected OneKey devices purchased between March 1 and October 12, 2026.
Ledger emphasized that its official sales channels and direct sales remain unaffected. The investigation continues as the Donjon team examines additional devices submitted by customers and assesses whether similar modifications appear in other models or regions.
Security Guidance for Customers
Ledger issued specific instructions for users who purchased signers through CryptoBilis. Anyone who has not yet initialized their device should avoid setting it up and contact Ledger Support immediately. Customers who have already used an affected signer must transfer their cryptocurrency to a new device initialized with a completely fresh recovery phrase. Users are explicitly warned against importing or restoring an existing recovery phrase on any device purchased from CryptoBilis.
For customers who experienced losses, Ledger directs them to report the incident through official support channels and contact local law enforcement. Suspected tampered devices should not be opened or sent to third parties without first consulting Ledger Support or authorities. The company reiterated that it never contacts customers, sends unsolicited messages, or requests recovery phrases.
Customers who obtained Ledger devices through other channels received inspection guidance from the manufacturer. The advice includes backing up recovery phrases securely before any opening and warns that disassembly can damage the device.
Investigation Ongoing Beyond CryptoBilis
Ledger confirmed the implant in one affected signer on October 10 and stated that every verified loss involves devices bought through CryptoBilis. The company has not established how the components entered the devices or identified the individuals responsible. No arrests or charges have been announced.
Although confirmed incidents involve CryptoBilis products, Ledger continues reviewing reports of hardware modifications in other devices and locations. The Donjon team specializes in physical attacks against cryptocurrency signing hardware and will analyze submitted devices to determine if additional implants exist.
The manufacturer has requested submissions of relevant evidence, including physical modifications, to a dedicated email address. Customers with suspected issues should reach out to Ledger Support, and law enforcement coordination is advised before opening any devices.
Disclaimer
This article was generated by AI using information from multiple industry sources. It has not been reviewed or verified by a human editor and may contain inaccuracies, omissions, or misinformation. Readers are encouraged to independently verify any information before making decisions based on its content.Tired of the noise?
Let the bots trade for you.
Trade 24/7, without emotion, with data-driven strategies.
Associated articles
Ledger Confirms Hardware Implant in CryptoBilis Devices Linked to Tens of Millions in Losses
Ledger Halts European Hardware Wallet Sales After Implant Claims
Ledger Investigates $87M Crypto Wallet Theft Linked to Reseller

Ledger Denies Hack After OneKey Reproduces Outdated Ethereum App Flaw

CZ Urges Crypto Holders to Diversify Wallets After $70 Million Coldcard Exploit
Latest articles
Google Rolls Out Gemini 4 Argon AI Model With Cybersecurity Focus and Competitive Pricing
France Weighs 31.4% Tax on Crypto Swaps Into Regulated Stablecoins From 2027
Polymarket CEO Teases On-Chain Asset at TOKEN2049, Sparking Token and Airdrop Talk
US September CPI Climbs to 3.7% as Core Inflation Exceeds Forecasts